Asos hackers reached Snowflake through an employee's login, City AM reports
Attackers who threatened millions of Asos customers got into its Snowflake-hosted data by posing as an employee's trusted contact, City AM reports. Its report names ShinyHunters for H&M alone among Asos, H&M and TFG, so a shared method across the three is unconfirmed.
The Board Room · Leadership desk
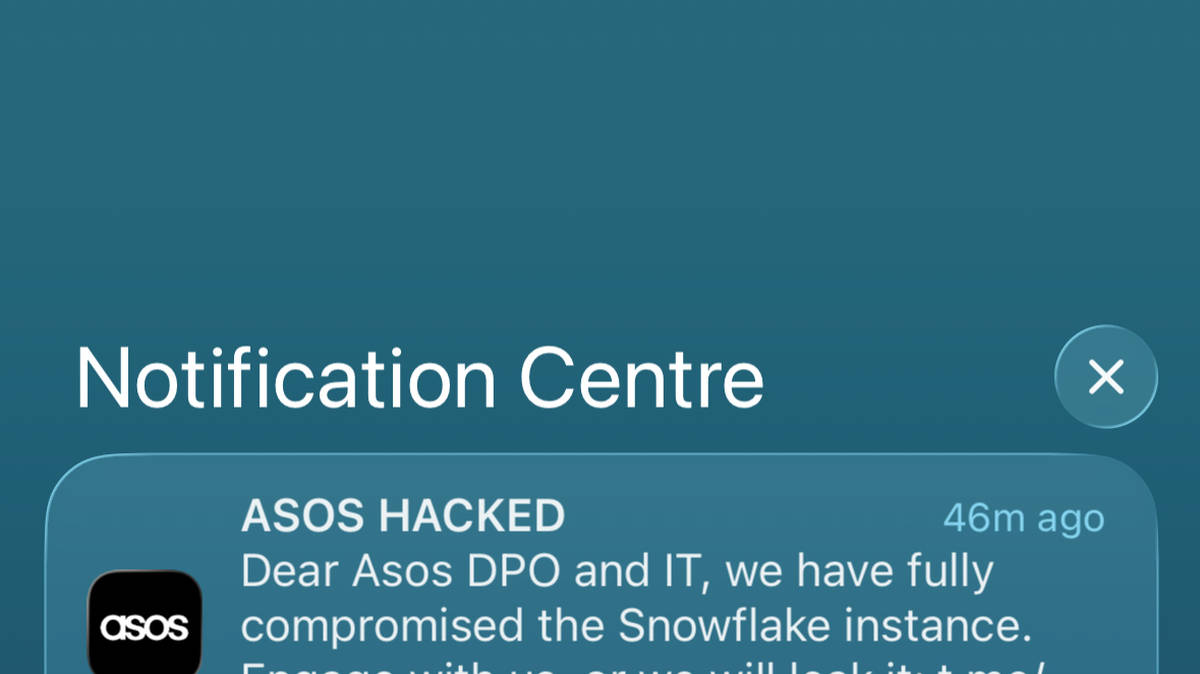
Co-op said the incident cost it £206m in revenue. M&S and Co-op attacks began with IT workers tricked out of credentials. Asos says no payment data was stolen; its attackers claim worse. A push alert threatened to leak Asos customers' data. The Works told staff to be vigilant.
- cost Co-op Said the incident cost it £206m in revenue, claim 8
- precedent M&S and Co-op Their attacks began in a similar way, with IT workers tricked into giving away their credentials, claim 6
- contradiction Asos Says no payment information was stolen; the group behind the incident claims the breach was worse, claim 16
- exposure Asos customers A push notification threatened to leak information belonging to the company's millions of customers, claim 1
- decision The Works Contacted staff the day after the Asos breach to remind them to be vigilant, it is understood, claim 13
| Who | How | Kind | Claim |
|---|---|---|---|
| Co-op | Said the incident cost it £206m in revenue | cost | 8 |
| M&S and Co-op | Their attacks began in a similar way, with IT workers tricked into giving away their credentials | precedent | 6 |
| Asos | Says no payment information was stolen; the group behind the incident claims the breach was worse | contradiction | 16 |
| Asos customers | A push notification threatened to leak information belonging to the company's millions of customers | exposure | 1 |
| The Works | Contacted staff the day after the Asos breach to remind them to be vigilant, it is understood | decision | 13 |
What happened
- Asos has told customers that no payment information was stolen and that the app is safe, while the group behind the incident claims the breach is worse than the company says.
- H&M said days later that it was investigating claims of a hack, and the group named in those claims, ShinyHunters, is being pursued by the FBI.
- TFG said IT systems and websites at some brands, including Phase Eight, Hobbs and Whistles, were affected, with "no reason to believe that payment information is at risk".
- The M&S and Co-op attacks last spring began in a similar way, with IT workers tricked into giving away their credentials.
Why it matters
- constraint A review confined to a platform vendor's own settings would miss the path reported at Asos, so access checks have to test whether staff can be talked into releasing a login.
- decision Who approves customer wording while a breach's scope is disputed is a decision for this quarter, because Asos's attackers contradict the company in public. Settled now, it gives next quarter's first incident a script; unsettled, the wording gets negotiated while the attackers' version circulates.
- cost Co-op's £206m revenue loss from last spring's incident is the scale of downside in this sector, and City AM says that retailer and its peers are still recovering.
The reported weak point at Asos was a login, and that sets what a review of third-party platforms has to cover. City AM describes Snowflake as a service where retailers store basic customer information and send push notifications, and the hackers say that is where they got into Asos [15]. The threat itself reached customers as a push notification [1]. City AM does not say how that message was sent. If one credential opens both the stored data and the push function, a stolen login gives an attacker the data and a direct line to customers. That link is our inference.
Spending is already large. The British Retail Consortium's chief executive, Helen Dickinson, said UK retailers put hundreds of millions of pounds a year into their cyber defences [9]. She also said: "Cyber-attacks are a very real risk for all businesses and are becoming increasingly sophisticated" [10]. City AM's own point is narrower: FTSE 100 firms like Tesco can easily pile cash into complex systems, yet attacks often rely on old-fashioned human error [11]. In our view the Asos account fits that description better than "sophisticated", because the reported method was impersonation [5].
Other retailers have reacted to the Asos incident [12][13]. The Works, an Aim-listed toys and crafts seller, contacted its staff the day after the Asos breach to remind them to be vigilant, it is understood [13]. Tesco chief executive Ken Murphy said: "We will obviously seek to learn from any incident, including the Asos incident, to make sure that we are staying on top of that" [12].
The attribution is thinner than a run of linked breaches implies. City AM names ShinyHunters in only one of the three cases, and there as a claim H&M said it was investigating [3][14]. The Asos attackers appear as "the group behind the incident" [16], and TFG called its event a "cybersecurity incident" [4]. A shared method across the three stays an inference until a company or an investigator says so.
Some shoppers read the Asos threat as promotion. One wrote on X that it was "some crappy marketing scheme to get me to check the app and to view their snowflake collection" [2]. Customers who cannot tell an attacker's alert from a retailer's own marketing cannot be told to distrust alerts without also discounting the retailer's real ones.
What to watch
- Whether H&M's investigation confirms the ShinyHunters claim, and whether Asos or TFG attribute their incidents to any named group.
- Whether Asos revises its statement on payment data after the attackers' claim that the breach is worse than the company says.
- Whether Asos or Snowflake describe what protected the compromised employee login, and whether the push function sat behind the same credential.
Clarity's read
What the record supports and how the coverage leans. The claims behind it follow.
Reality
- Evidence40
- Adoption
- Insufficient
- Hype gap+10
- Incentives
- Insufficient
- Confidence45
Claim ledger
Ranked by verification strength, evidence, and original report placement.
- [1]
Asos customers were sent a cryptically worded push notification that was a direct threat to Asos's management, threatening to leak information belonging to the company's millions of customers.
- [2]
Some shoppers thought the alert was marketing; one wrote on X that it was "some crappy marketing scheme to get me to check the app and to view their snowflake collection".
- [3]
Days later, H&M said it was investigating claims that ShinyHunters, a global criminal hacking group currently being pursued by the FBI, had hacked into its servers.
- [4]
TFG, the Johannesburg-listed owner of brands including White Stuff, said it was aware of a "cybersecurity incident" at its London business; IT systems and websites of some brands, including Phase Eight, Hobbs and Whistles, were impacted, and it said there was "no reason to believe that payment information is at risk".
- [5]
Asos's hackers gained access to its Snowflake systems by posing as a "trusted contact" of an employee to obtain their login information.
- [6]
The attacks on M&S and Co-op began in a similar way, as IT workers were tricked into giving away their credentials.
- [7]
Co-op, Marks and Spencer and Harrods were hit with data breaches in spring of last year, and these retailers are still recovering.
- [8]
Co-op said the incident cost it £206m in revenue.
- [9]
Helen Dickinson, chief executive of the British Retail Consortium, said UK retailers spend hundreds of millions of pounds every year on their cyber defences.
- [10]
Helen Dickinson said: "Cyber-attacks are a very real risk for all businesses and are becoming increasingly sophisticated."
- [11]
While FTSE 100 firms like Tesco can easily pile cash into shoring up their cyber defences with complex systems, cyber attacks often rely on old-fashioned human error.
- [12]
Tesco chief executive Ken Murphy said: "We will obviously seek to learn from any incident, including the Asos incident, to make sure that we are staying on top of that."
- [13]
Aim-listed toys and crafts seller The Works contacted its staff the day after the Asos breach to remind them to be vigilant, it is understood.
- [14]
Of Asos, H&M and TFG, the report names ShinyHunters in connection with one retailer (H&M); the Asos attackers and the TFG incident are not tied to a named group.
- [15]
The hackers say they gained access to Asos's servers on Snowflake, a cloud platform service that allows retailers to store basic customer information and send push notifications.
- [16]
Asos has tried to reassure customers that no payment information was stolen and that the app remains safe to use, but the group behind the incident have claimed the data breach was worse than the company is making out.
Get this ledger inside ChatGPT. Ask about any of our stories and the answer brings its figure, each claim’s verdict and the sources. Free, no account.
Sources
1 independent publisher whose own reporting we read for this story.
- cityam.comRetailers back on alert after new wave of cyber attacks
1 article · October 14, 2026
Topics and entities
Follow any of these and your For You feed starts watching them — no settings page required.