SecurityIndependently confirmed2 publishers2 min readPublished Updated
iRhythm notifies at least 360,000 patients after a social engineering breach of hosted apps
iRhythm, maker of the Zio patch, says attackers who social-engineered access to third-party-hosted apps took data on at least 360,000 patients. The records link patients' insurance numbers to their device serial numbers, enough detail for a caller to pass as the company.
The Watch · Security desk
Bar comparison of people iRhythm said had information stolen: Texas, 298,647 people; South Carolina, 69,526 people.
People iRhythm said had information stolen, by state In people
| Item | Value | Claim |
|---|---|---|
| Texas | 298,647 people | 4 |
| South Carolina | 69,526 people | 5 |
What happened
- Investigators found the intruders had access to iRhythm's systems from June 3 to June 8.
- In a June 8-K, iRhythm told the SEC that a threat actor demanded payment in exchange for not publicly disclosing the stolen information.
- The exposed fields also include names, addresses, phone numbers, dates of birth, patient account numbers and dates of service.
Why it matters
- exposure Patients were exposed even though the devices and clinical systems were not touched, because their records were in hosted business applications that one social engineering attack could reach.
- decision Device makers keeping insurance and account data in third-party-hosted business apps have to treat every account on those apps as a route to protected health information.
- cost With iRhythm reporting no financial or operational hit, the cost of this breach falls on the patients whose records an extortionist now holds.
The two state filings already exceed the company's floor of 360,000 [1]. The Texas and South Carolina notices alone total 368,173 people [20], and that is before any count from California, where iRhythm also filed [6]. A company spokesperson declined to give the full number, telling Recorded Future News that iRhythm "responded promptly after detecting the unauthorized access and, once the scope was verified, notified affected individuals and applicable regulators." [7]
During the intrusion, iRhythm says, the attackers accessed and downloaded the data [12]. Its June 8-K said the company "received communications from a threat actor claiming to have obtained sensitive information, including proprietary data, patient protected health information and other personal information." [15] "Since receipt of the communications, the Company has confirmed that certain data was exfiltrated from those applications," iRhythm said [17].
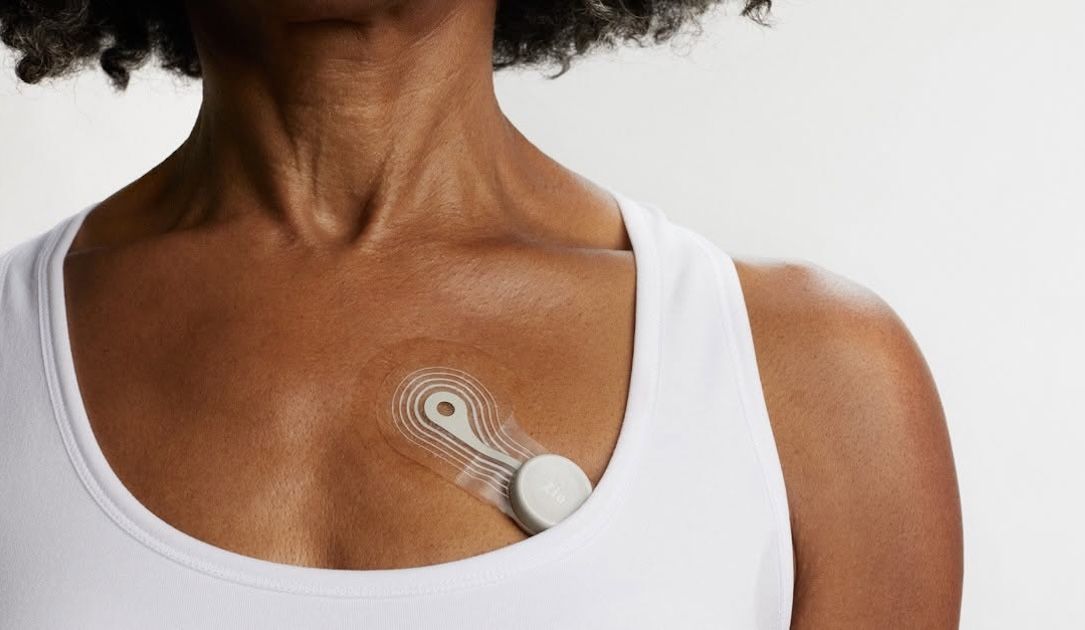
iRhythm's best-known product is the Zio Patch, a chest-worn sensor for long-term cardiac monitoring and arrhythmia detection [3]. "The incident did not affect iRhythm clinical systems or medical devices and did not result in a loss of service or disruption to operations," the spokesperson said [8]. The company says products, manufacturing and distribution were untouched and its finances were not disturbed. It reported $224.2 million in Q2 revenue [14]. The patient records were held somewhere else, in business applications hosted by a third party [10].
Disclosure came in two stages. Investors read about the extortion claim in the June 8-K [15]. Patients and state regulators are getting counts and letters through notices iRhythm began filing this week, according to The Record [2]. The applications and their host have not been named [10]. On the current record, the attackers got in by social engineering their way into access to those applications [10].
The Record counts dozens of medical device makers hit over the last two years, in incidents that reached business and manufacturing systems [18]. It lists Medtronic, Boston Scientific, Stryker, UFP, Masimo, Surmodics, Artivion and Zoll among those whose attacks leaked data on millions and caused supply chain problems [19]. No group has publicly claimed the iRhythm attack [13]. With operations intact, the only pressure on iRhythm was the stolen data [14][16]. The company says it has "no evidence that any personal information has been or will be used to commit identity theft." [21]
What to watch
- A California total, or filings in other states, that pushes the count past the 368,173 already listed in Texas and South Carolina.
- Disclosure of which hosted applications were entered and who runs them; matching intrusions at other customers of that provider would point to a supplier pattern.
- Publication of the stolen data, or a claim of responsibility by a named group.
Clarity's read
What the record supports and how the coverage leans. The claims behind it follow.
Reality
- Evidence65
- Adoption
- Insufficient
- Hype gap0
- Incentives
- Insufficient
- Confidence68
Claim ledger
Ranked by verification strength, evidence, and original report placement.
- [1]
Medical device maker iRhythm said the data of at least 360,000 people was breached in a June cyberattack.
- [2]
iRhythm began filing breach notices in multiple states this week, telling regulators and victims that the incident occurred on June 8 and involved unauthorized access to third-party systems.
ReportedSupportedSource: The Record (Recorded Future News)2 sources— create a free account to open themView cited source - [3]
iRhythm is best known for Zio Patch, a sensor patients wear on their chest for long-term continuous cardiac monitoring and heart arrhythmia detection.
- [4]
iRhythm said 298,647 people in Texas had information stolen.
- [5]
iRhythm said 69,526 people in South Carolina had information stolen.
- [6]
iRhythm also filed breach notices in California.
- [7]
A company spokesperson declined to say the full number of victims, telling Recorded Future News that iRhythm "responded promptly after detecting the unauthorized access and, once the scope was verified, notified affected individuals and applicable regulators."
ReportedSupportedSource: iRhythm spokesperson, to Recorded Future News2 sources— create a free account to open themView cited source - [8]
"The incident did not affect iRhythm clinical systems or medical devices and did not result in a loss of service or disruption to operations," the spokesperson said.
ReportedSupportedSource: iRhythm spokesperson2 sources— create a free account to open themView cited source - [9]
An investigation found hackers had access to company systems between June 3 and June 8.
- [10]
The hackers gained access to unidentified third-party-hosted business applications through a social engineering attack.
- [11]
Stolen information includes names, addresses, phone numbers, iRhythm patient account numbers, iRhythm device serial numbers, patient insurance numbers, dates of service and date of birth.
- [12]
The cybercriminals accessed and downloaded the information, according to a statement from iRhythm.
ReportedSupportedSource: iRhythm statement2 sources— create a free account to open themView cited source - [13]
No hacking group ever publicly took credit for the attack.
- [14]
The cyberattack did not impact iRhythm's products, devices, manufacturing process or distribution operations, iRhythm said its finances were not disturbed, and the company reported $224.2 million in Q2 revenue.
- [15]
In a June 8-K filing with the SEC, iRhythm said it "received communications from a threat actor claiming to have obtained sensitive information, including proprietary data, patient protected health information and other personal information."
ReportedSupportedSource: iRhythm 8-K filing2 sources— create a free account to open themView cited source - [16]
"The communications from the threat actor demanded payment in exchange for not publicly disclosing this information," the company said.
- [17]
"Since receipt of the communications, the Company has confirmed that certain data was exfiltrated from those applications," iRhythm said.
- [18]
Medical device companies have been hit by cybercriminals over the last two years, with dozens experiencing cybersecurity incidents that impacted business and manufacturing systems.
- [19]
Cyberattacks on Medtronic, Boston Scientific, Stryker, UFP, Masimo, Surmodics, Artivion and Zoll have leaked the sensitive medical data of millions and caused supply chain issues.
- [20]
The Texas and South Carolina notices together count 368,173 people.
- [21]
iRhythm said it has "no evidence that any personal information has been or will be used to commit identity theft."
Sources
2 independent publishers whose own reporting we read for this story.
- securityweek.comiRhythm Data Breach Impacts at Least 360,000 People
1 article · October 12, 2026
- therecord.mediaHundreds of thousands impacted by data breach at biosensor firm iRhythm
1 article · October 9, 2026
Topics and entities
Follow any of these and your For You feed starts watching them — no settings page required.