InvestNot yet confirmed elsewhere1 publisher2 min readPublished
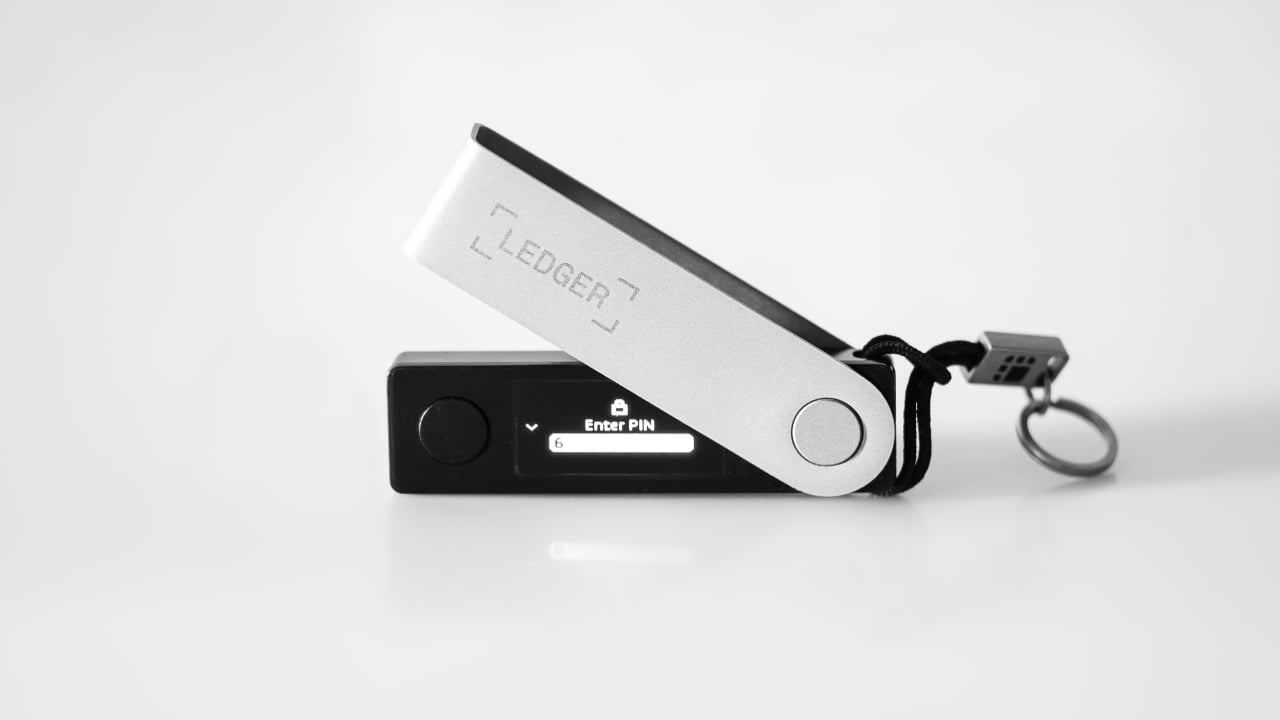
A MediaMarkt Ledger may carry an early build of the implant behind Asia's estimated $93.4 million in thefts
X user Johannes says his MediaMarkt Ledger holds an early version of the implant tied to an estimated $93.4 million in Asian losses. Ledger has not confirmed the link or the estimate, so retail buyers have no official answer on provenance.
The Investor · Invest desk
Four figures: Yfarmx's estimate averages about $198,300 per address, across 471 addresses by Yfarmx's count. The total, $93.4 million, has not been confirmed by Ledger. Ledger advised CryptoBilis buyers from the past 90 days to consider moving assets to a new Ledger.
| Figure | Value | Note | Claim |
|---|---|---|---|
| Average loss per address | $198,300 | Approximate, from Yfarmx estimate | 14 |
| Addresses hit (Yfarmx count) | 471 addresses | 6 | |
| Estimated losses (Yfarmx) | $93,400,000 | Ledger has not confirmed | 7 |
| CryptoBilis purchase window | 90 days | Advice: consider moving to a new Ledger | 3 |
What happened
- CryptoBilis devices were modified after the reseller changed owners, letting attackers read the seed phrase while the device still passes authenticity checks.
- Ledger asked CryptoBilis to suspend sales and shipments as a precaution.
- No funds have been taken from the European device, according to the report.
Why it matters
- exposure A passing authenticity check no longer clears a device, so for any owner the seller and purchase date are the evidence left to check.
- constraint Ledger's advice to move assets covers CryptoBilis purchases from the past 90 days, so a retail-chain buyer has no instruction to follow. The only channel action in the report is the sales suspension at one reseller.
- decision Holders and custodians who bought a Ledger at retail must decide whether to move funds on a report Ledger has not confirmed. In our view the purchase record is what to verify first.
The case for a European spread is one buyer's photographs and one investigator's reading of an antenna label [8][13]. Johannes, who says he bought the device two weeks ago [8], offered two explanations of his own: "Either the device didn't work, or they were waiting for a more widespread usage of the compromised devices," he said [11].
By his account the purchase predates the thefts that surfaced in Asia late last week [15]. That fits Cointelegraph's description of the implant as appearing to be an earlier version of the one found in CryptoBilis devices [9].
Yfarmx's estimate works out to about $198,300 an address [14], an average, and one Ledger has not confirmed [7]. In our view that makes waiting affordable for an attacker, because each address that eventually empties is worth roughly that much. It also makes Johannes's second explanation untestable until funds move.
Mark Karpeles, the former Mt Gox chief executive whose investigations into the Asian devices helped expose the problem, said the device's antenna marks it as the "Eurasian version" [13]. According to the report, that suggests separate implant versions went to regions that use different mobile frequencies [13]. Two hardware variants are harder to explain as one modified unit, so we think the evidence leans toward a problem wider than a single reseller.
That lean rests on one device. The simpler account is an isolated unit that reached a MediaMarkt shelf by a path the report does not describe, and our view fails if Ledger or MediaMarkt shows that, if a second unit is opened and carries a different component, or if the antenna label turns out to mean something other than a regional variant. A drained European address would settle it the other way.
What to watch
- A Ledger statement confirming or ruling out that the MediaMarkt unit belongs to the same attack.
- A second independent report of a tampered device from European retail, or a drained European address.
- Any reconciliation of Ledger's word "limited" with Yfarmx's $93.4 million across 471 addresses.
Clarity's read
What the record supports and how the coverage leans. The claims behind it follow.
Reality
- Evidence30
- Adoption
- Insufficient
- Hype gap+20
- Incentives
- Insufficient
- Confidence35
Claim ledger
Ranked by verification strength, evidence, and original report placement.
- [1]
Devices from the official reseller CryptoBilis, which had recently been sold to a new owner, were found modified in a way that apparently lets attackers read the seed phrase and steal funds even though the device can still pass authenticity checks.
- [2]
Ledger asked CryptoBilis to suspend sales and shipments of its devices as a precaution.
- [3]
Ledger advised customers who had purchased devices from CryptoBilis within the past 90 days to consider transferring their assets to a new Ledger.
- [4]
Ledger said in its most recent update: "The volume of impacted devices is limited."
- [5]
The attack hit Ledger devices in Asia late last week.
- [6]
Cybersecurity outlet Yfarmx estimated the losses from the tampered Ledger attack at $93.4 million across 471 addresses.
ReportedInsufficientSource: Cointelegraph, citing Yfarmx2 sources— create a free account to open themView cited source - [7]
Ledger has not confirmed the Yfarmx $93.4 million loss figure.
ReportedInsufficientSource: Cointelegraph2 sources— create a free account to open themView cited source - [8]
X user Johannes presented photographs of a tampered Ledger he said he purchased two weeks ago from the European consumer electronics chain MediaMarkt.
ReportedInsufficientSource: Cointelegraph, citing X user Johannes2 sources— create a free account to open themView cited source - [9]
According to the report, the implant inside the reported European device appears to be an earlier version of the one found linked to CryptoBilis shipped devices in Asia.
ReportedInsufficientSource: Cointelegraph2 sources— create a free account to open themView cited source - [10]
No funds have been taken from the reported European device.
ReportedInsufficientSource: Cointelegraph, relaying Johannes's report2 sources— create a free account to open themView cited source - [11]
Johannes said: "Either the device didn't work, or they were waiting for a more widespread usage of the compromised devices."
ReportedInsufficientSource: X user Johannes, quoted by Cointelegraph2 sources— create a free account to open themView cited source - [12]
Ledger has not confirmed the reported European device is part of the same attack.
ReportedInsufficientSource: Cointelegraph2 sources— create a free account to open themView cited source - [13]
Former Mt Gox CEO Mark Karpeles, whose investigations into the tampered Asian Ledgers helped bring the problem to light, said the antenna in the device says it is the "Eurasian version", suggesting separate versions of the implant have been sent to regions that use different mobile frequencies.
- [14]
Yfarmx's estimated $93.4 million across 471 addresses averages about $198,300 per address.
- [15]
By Johannes's own account, his purchase two weeks ago falls before the Asian thefts surfaced late last week.
Sources
1 independent publisher whose own reporting we read for this story.
- cointelegraph.comLedger attack spreads to EU, AI finds ’18 trillion XRP’ bug: Hodler’s Digest
1 article · October 11, 2026
Topics and entities
Follow any of these and your For You feed starts watching them — no settings page required.