SecurityNot yet confirmed elsewhere1 publisher3 min readPublished
Flock becomes the CVE authority for its own license plate readers and cameras
Flock became one of more than 550 CVE Numbering Authorities, able to assign and grade CVEs for its own license plate readers and cameras. It earlier deemed a set of physical-access flaws not material.
The Watch · Security desk
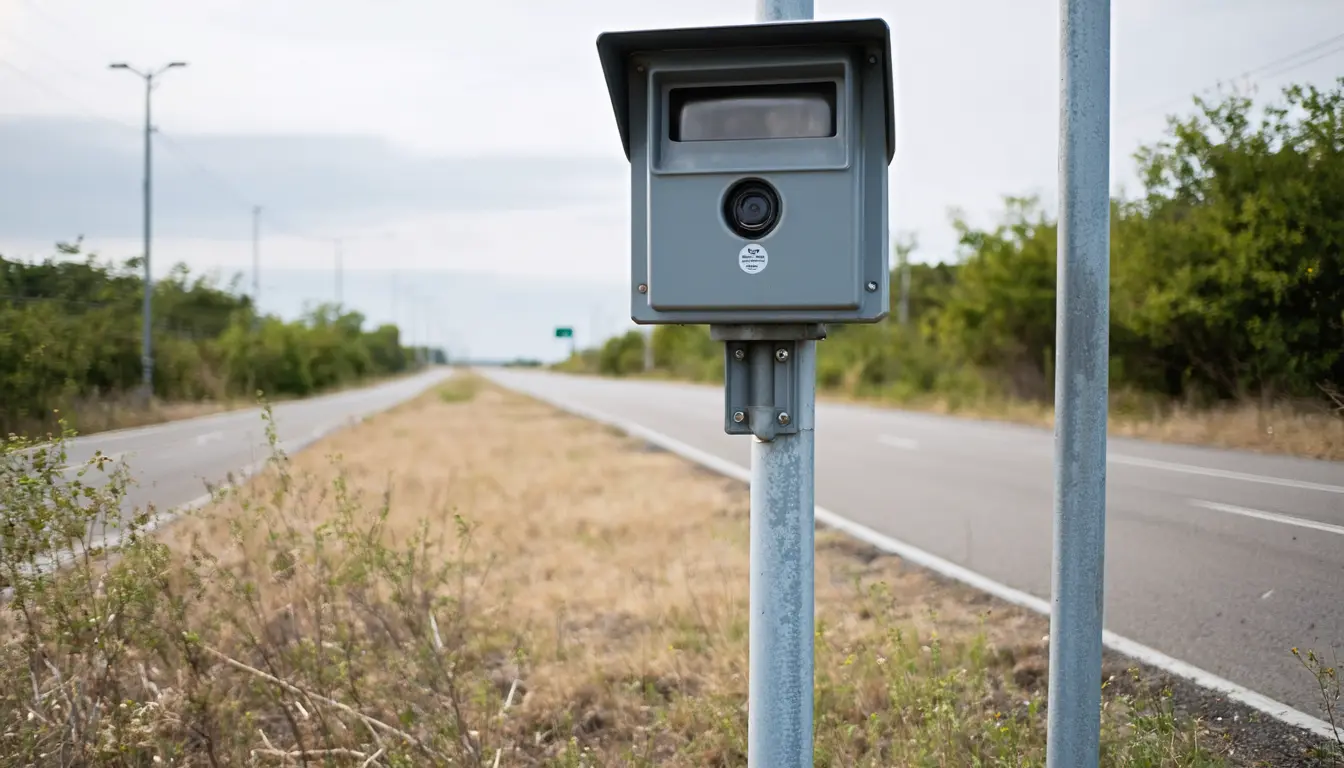
Flock grades CVEs in its own products and can hold back publication over safety risk. Last year it deemed physical-access defects not material. Its policy bars physical attacks. Moussouris: records should let cities and police track risks. Edwards expects some uncoordinated disclosure.
- capability Flock as a CNA Assigns CVE IDs to flaws in its own products and grades them as a CVE Numbering Authority, claim 1
- decision Flock, on publication Policy reserves the right to hold back publication if disclosure would create a safety risk, claim 10
- precedent Flock, last year Deemed researchers' reported defects not material because they require physical access to the device, claim 7
- constraint Flock's disclosure policy Disallows physical attacks, live customer deployment testing and social engineering; no paid bug bounty, claim 9
- exposure Cities and police departments Moussouris: Flock's measure as a CNA is whether its records let them track specific risks, claim 13
- exposure Researchers Edwards expects some to continue disclosing Flock vulnerabilities without coordinating with the company, claim 14
| Who | How | Kind | Claim |
|---|---|---|---|
| Flock as a CNA | Assigns CVE IDs to flaws in its own products and grades them as a CVE Numbering Authority | capability | 1 |
| Flock, on publication | Policy reserves the right to hold back publication if disclosure would create a safety risk | decision | 10 |
| Flock, last year | Deemed researchers' reported defects not material because they require physical access to the device | precedent | 7 |
| Flock's disclosure policy | Disallows physical attacks, live customer deployment testing and social engineering; no paid bug bounty | constraint | 9 |
| Cities and police departments | Moussouris: Flock's measure as a CNA is whether its records let them track specific risks | exposure | 13 |
| Researchers | Edwards expects some to continue disclosing Flock vulnerabilities without coordinating with the company | exposure | 14 |
What happened
- The policy disallows physical attacks, testing against live customer deployments, access to law enforcement data, denial-of-service testing and social engineering, and Flock runs no paid bug bounty.
- Researchers reported multiple defects in Flock's license-plate reader and gunshot detection system last year, and Flock deemed them not material because they require physical access.
- Flock's business has drawn public and legal scrutiny over privacy and multiple reports of police abusing the technology, CyberScoop reported.
Why it matters
- exposure Cities and police departments that track risk through Flock's records will see a description and severity score written by Flock alone.
- contradiction Flock's CISO promises customers a single trusted source, yet the company's one documented call so far dismissed flaws in devices that sit on public poles, as Moussouris pointed out.
- constraint Flock can hold back a record when it judges disclosure a safety risk, and few CNA norms limit that judgment.
- decision Researchers must now choose between coordinating with Flock and publishing alone, and Edwards expects some to publish alone.
The CNA role itself is common. Zach Edwards, a security and privacy researcher, is dubious about Flock holding it, but he adds that many vendors, including some offering similar products, are already in the program [11]. Katie Moussouris of Luta Security made the case for vendor-run CNAs: "Vendors make sense as CNAs for their own products if they can be trusted to maintain accurate records. They know the code, they can confirm the flaw, and they can tie the record to affected versions and the fix," she said [17].
The same job carries the risk. "A vendor in the CNA role writes the description and often sets the severity score, so an immature vendor may inaccurately represent an issue, either through ignorance or in a misdirected effort to downplay it," Moussouris said [16]. Edwards called CNAs "essentially grading their own homework" [15].
Flock has one documented decision of this kind, and it predates the role. Researchers last year reported multiple defects in its license-plate reader and gunshot detection system. Flock submitted them for inclusion in the National Vulnerability Database but deemed them not material because they require physical access [7]. "These cameras sit on poles on public streets," Moussouris said [8]. Flock's disclosure policy also disallows physical attacks in testing [9]. On the sources' account, the class of flaw Flock has already graded as immaterial is a class its policy tells researchers not to probe.
The policy also reserves the right to hold back publication if Flock decides disclosure would create a safety risk to law enforcement or the public [10]. Moussouris said: "The latter may lead to an abuse in their authority and control of CVEs unless they embrace a more mature customer-safety-first stance of timely, transparent, and accurate vulnerability disclosure" [18]. CyberScoop reports there are relatively few norms for how CNAs operate, because responsibility comes down to each participating vendor [12].
Flock's own account is short. Chris Castaldo, its chief information security officer, said the authority "allows us to move faster when researchers report findings, eliminate confusion from duplicate or conflicting vulnerability entries and give our customers a single, trusted source for security information about our products" [3]. Flock declined to answer CyberScoop's questions or make an executive available, and referred the outlet to a blog post [5]. It published its disclosure policy in August and recently created a security advisories page for newly discovered and confirmed vulnerabilities [6].
In our view, the physical-access ruling and the withholding clause are the two places where a Flock record could depart from what a city needs. Moussouris set a test that anyone can check: "The measure of Flock as a CNA is whether its records give cities, police departments, and the public enough detail and accuracy to let people track specific risks by product version, the nature of the vulnerability, and ideally how to mitigate or fix it" [13]. CyberScoop also notes that Flock's business has drawn public and legal scrutiny over privacy and multiple reports of police abusing the technology, and that this scrutiny could cloud how researchers view it as a CNA [4].
Edwards noted that activists have already done technical teardowns of Flock's products. He expects some researchers to keep disclosing Flock vulnerabilities without coordinating with the company [14].
What to watch
- The first CVE records Flock issues, and whether they name affected versions, severity and fixes as Moussouris's test requires.
- Whether Flock's security advisories page lists physical-access flaws like those it earlier deemed not material.
- Whether researchers keep publishing Flock vulnerabilities without coordination, as Edwards expects.
Clarity's read
What the record supports and how the coverage leans. The claims behind it follow.
Reality
- Evidence55
- Adoption
- Insufficient
- Hype gap
- Insufficient
- Incentives70
- Confidence55
Claim ledger
Ranked by verification strength, evidence, and original report placement.
- [1]
Flock gained authority to assign CVE IDs to vulnerabilities in its own products and to grade those defects as a CVE Numbering Authority.
- [2]
Flock, a maker of surveillance systems including automated license plate readers and AI-powered cameras, said it joined the global footprint of more than 550 CNAs.
- [3]
"It allows us to move faster when researchers report findings, eliminate confusion from duplicate or conflicting vulnerability entries and give our customers a single, trusted source for security information about our products," Chris Castaldo, chief information security officer at Flock, said in a statement.
- [4]
Flock's business has drawn considerable public and legal scrutiny over privacy concerns, along with multiple reports of police abusing the technology, and the controversies have impacted its credibility and could cloud how security researchers view it as a CNA.
- [5]
Flock declined to answer questions or make an executive available for an interview, and instead referred CyberScoop back to a blog post.
- [6]
Flock published its vulnerability disclosure policy in August and recently created a security advisories page where it will publish all newly discovered and confirmed vulnerabilities going forward.
- [7]
Researchers last year reported multiple defects in Flock's license-plate reader and gunshot detection system, which the company submitted for inclusion in the National Vulnerability Database but deemed not material because the vulnerabilities require physical access to the device.
- [8]
"These cameras sit on poles on public streets," Moussouris said.
- [9]
Flock's vulnerability disclosure policy specifically disallows testing against live customer deployments, accessing law enforcement or investigative data, physical attacks, denial-of-service testing or social engineering. The company does not run a paid bug bounty program.
- [10]
Flock's policy reserves the right to hold back publication if it decides disclosure would create a safety risk to law enforcement or the public.
- [11]
Edwards is dubious about Flock's position as a CNA, but adds that many vendors, including some offering similar products, are already in the program.
- [12]
There are relatively few norms in how CNAs operate because the responsibility ultimately comes down to each participating vendor.
- [13]
"The measure of Flock as a CNA is whether its records give cities, police departments, and the public enough detail and accuracy to let people track specific risks by product version, the nature of the vulnerability, and ideally how to mitigate or fix it," Katie Moussouris, founder at Luta Security, told CyberScoop.
- [14]
Zach Edwards, a security and privacy researcher, noted that numerous activists have done technical teardowns of Flock's products and said he expects some researchers to continue disclosing Flock vulnerabilities without coordinating with the company.
- [15]
Zach Edwards described CNAs as "essentially grading their own homework."
- [16]
"A vendor in the CNA role writes the description and often sets the severity score, so an immature vendor may inaccurately represent an issue, either through ignorance or in a misdirected effort to downplay it," Moussouris said.
- [17]
"Vendors make sense as CNAs for their own products if they can be trusted to maintain accurate records. They know the code, they can confirm the flaw, and they can tie the record to affected versions and the fix," Moussouris said.
- [18]
"The latter may lead to an abuse in their authority and control of CVEs unless they embrace a more mature customer-safety-first stance of timely, transparent, and accurate vulnerability disclosure," Moussouris said, of Flock's right to hold back publication.
Sources
1 independent publisher whose own reporting we read for this story.
- cyberscoop.comFlock can now issue CVEs for its own products. Should we trust it?
1 article · October 12, 2026
Topics and entities
Follow any of these and your For You feed starts watching them — no settings page required.
Topics
- Vulnerability DisclosureFollow
- CVE Numbering AuthoritiesFollow
- Surveillance TechnologyFollow