Security3 publishers3 min readPublished
WeedHack lost its C2 and kept its funnel: ten fake Minecraft sites still convert victims
McAfee says the WeedHack stealer's control server is dead and its renter dashboard gone, but ten impersonation sites and the search rankings behind them are still delivering victims.
The Watch · Security desk
What happened
- McAfee Labs says ten malicious sites and several file-hosting accounts are still distributing the WeedHack infostealer after its command-and-control infrastructure was disrupted.
- The company's WebAdvisor product blocked more than 6,300 attempts by its own users to reach those sites in the past month.
- The service had run a free tier open to anyone with a Discord account and a premium tier with webcam surveillance at $5 a month.
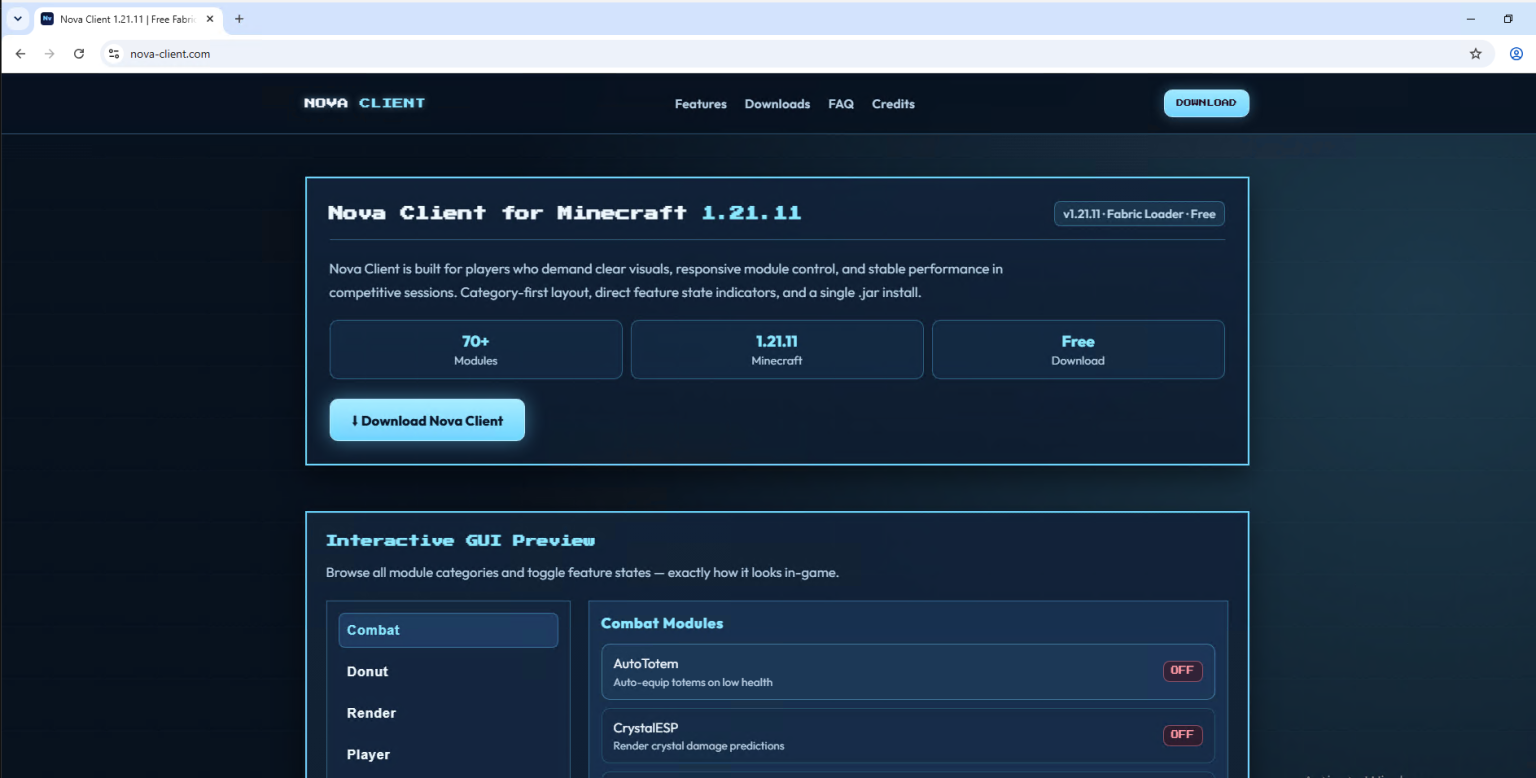
- Counterfeit Xenon Client and Nova Client sites sit at the top of Google, Bing, Brave and DuckDuckGo results, above the projects' GitHub and Modrinth listings.
- The delivered JAR payloads collect system information and add Microsoft Defender exclusions before stealing data from the host.
Compiled by The WatchSomething wrong?How this is made
Why it matters
- constraint Killing the control server and dashboard leaves the operators needing a new host, not a new audience; recovery for them is a rental, not a rebuild.
- cost The costly asset in this campaign is search position, and while it stands the victim count keeps accruing against a disruption already booked as a result.
- exposure Open-source Minecraft projects that never registered a domain have no brand estate to defend, and the impersonation ranks above the repository they do control.
- decision Because intake now runs on mainstream file-sharing and chat accounts plus rankings, the next meaningful takedown is a moderation and search decision rather than a hosting one.
The half of WeedHack that went dark is the half that is cheap to replace. McAfee says the operation pulled its live server address out of the Ethereum blockchain using EtherHiding, a design whose entire purpose is to make the loss of any single host survivable [8]. The vendor nonetheless reports that after its early-July writeup the C2 stopped answering and the renter-facing dashboard vanished [3]. What did not go anywhere is the acquisition layer: pages detailed enough to reproduce a real tool's feature list, FAQ, install steps, developer credits and links back to the genuine GitHub repository [9].
The June figures reward a little division. McAfee logged 116,464 infected systems since January and put daily intake at 2,000 to 3,000 [7]. At that rate the entire cumulative total represents 39 to 58 days of work [1], against roughly five months of operation, so the pace that made the original report alarming belongs to the period after the distribution network matured rather than to the malware's debut. The stealer was never the scarce input.
The 6,300 blocked attempts work out to about 210 a day [2], and that counts only McAfee-protected users bouncing off ten known domains [1][2]. It does not count JAR files hosted on Planet Minecraft and EndMods, both legitimate destinations for Minecraft tools [19], nor the link sprawl on the services doing most of the delivery: Discord at 49.6 percent of catalogued malicious URLs, MediaFire 23.4, GitHub 8.2, Dropbox 4.6 [16], which is 85.8 percent sitting on four platforms users have no reason to distrust [3].
The impersonation succeeds partly because much of the target ecosystem never had a website to impersonate. Nova Client is an open-source project without one, so the attackers built the missing site and ranked it above the repository [13]. McAfee's cleanest tell on that page is a credits section listing generic team names instead of the people who wrote the code [14]. Where a real site does exist, the clone sits on top of it: the first two Google results for "Xenon Client" led to fake sites, according to McAfee [11]. One domain in the set was assembled with the AI website builder Lovable, which puts the cost of the next convincing clone close to zero [15]. Volume is cheap by other routes too, with one Discord channel pushing fake DonutSMP clients carrying more than 1,900 members [17] and a single site listing eight separate mods that all delivered the same malware [18].
None of this is particular to Minecraft. Check Point documented a comparable operation in June 2026 that impersonated open-source and freeware projects and routed visitors through a traffic distribution system to deliver Remus Stealer and other families [21]. McAfee's own advice concedes where the leverage is by being a routing rule rather than a detection one: take mods from the developer's repository or from Modrinth and CurseForge, and read a prompt to disable antivirus as the payload identifying itself [20].
What to watch
- Whether the ten named domains lose registration or simply cycle out of the top results while replacements rank in their place.
- Whether a replacement C2 surfaces through the Ethereum lookup and daily infection counts return to the 2,000 to 3,000 range.
- Whether Discord, MediaFire, GitHub, Dropbox and Lovable act on the specific accounts and pages McAfee identified.