Product1 publisher3 min readPublished
LGT put hybrid post-quantum key exchange in front of live online banking customers
Christian Pfister says quantum safety entered the bank's risk meetings in 2022, and the live pilot's problems turned up in load balancers and content delivery networks along the path between customer and server.
The Product Desk · Product desk
What happened
- LGT Financial Services set up a Quantum Safe Competence Center joining security operations, architecture, public key infrastructure, application owners, vendors and risk stakeholders, led by Christian Pfister.
- The bank's online banking system is running a live hybrid key exchange pilot that pairs X25519 with the NIST-standardized ML-KEM, and Pfister said customers see no disruption.
- The testing broke outside the servers: some connections failed at load balancers and content delivery networks, and others returned to the previous configuration.
- Supplier engagement became its own workstream, pulling vendor management and procurement into asking about product roadmaps, supported algorithms, timelines and compatibility constraints.
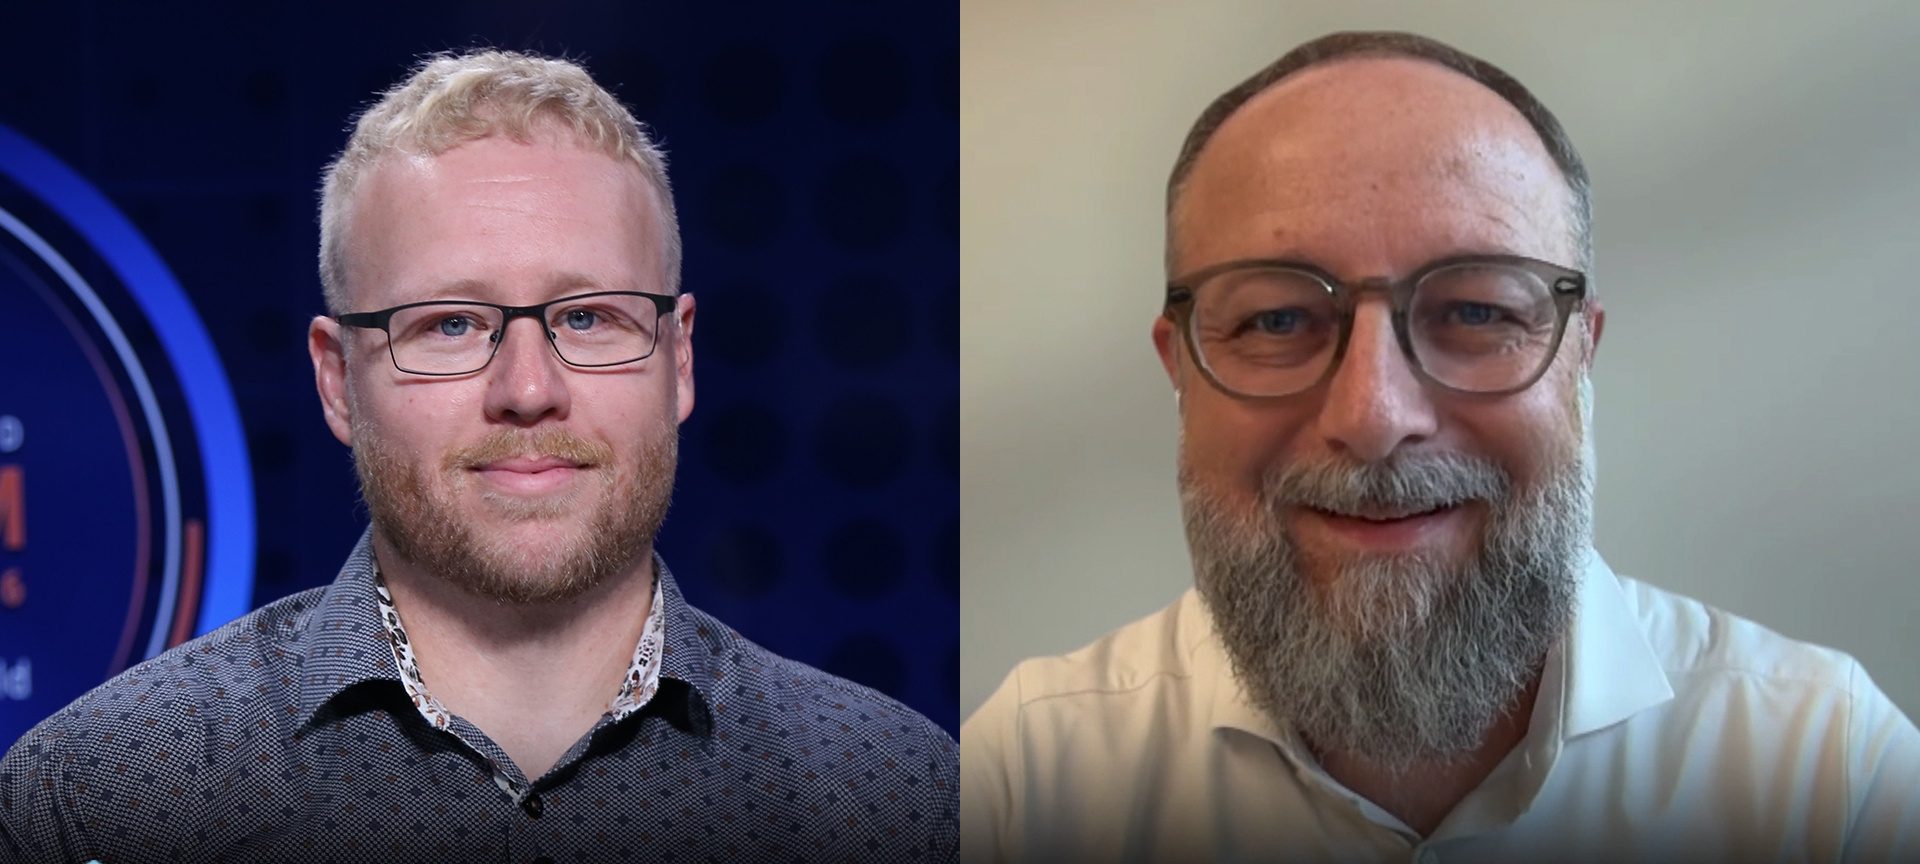
- Pfister described the program in an interview with DigiCert principal crypto architect Shane Kelly at DigiCert's World Quantum Readiness Day event.
Compiled by The Product DeskSomething wrong?How this is made
Why it matters
- constraint The competence center gives direction and the service owners make the changes, so the timetable belongs to whichever application owner or supplier moves last. The security team can measure progress but cannot set the dates.
- decision Procurement now holds a gate it did not have before: a supplier that will not commit to a supported-algorithm date sets the ceiling on how fast any wave can start.
- exposure The network and edge teams have to fix the breakage, and cryptography was never why they bought a load balancer or a CDN. The algorithm decision belongs to someone else.
- capability A retail bank running hybrid keys in production without customer disruption gives peers a scope they can copy: one customer-facing path, tested end to end, before the inventory is complete.
A customer signing into LGT's online banking cannot tell whether the session negotiated the post-quantum half of the handshake or used the classical one, and neither can an error dashboard. In testing, Pfister said, some connections failed and others returned to the previous configuration [9]. The fallback is what makes the pilot safe to run in production [8]. It also means success has to be measured as the share of sessions that actually negotiated ML-KEM, because a downgraded connection still logs the customer in.
Pfister put the failures in a familiar category. Legacy hardware, unsupported firmware and unmanaged libraries are familiar to everyone, he said, and the pilot exposes technical debt that already exists. That is not a reason to wait, in his account; it is why starting early matters for the bank [10].
The technical work started before the inventory was finished: a modernized TLS baseline, then the X25519 and ML-KEM pairing in controlled environments [7][3]. "If you try to inventory, replace and validate every cryptographic use case at once, it makes the program unmanageable, and you can't measure the outcome," Pfister said [4]. On sequencing he was blunter: the post-quantum cryptography migration is not one project and one algorithm change, he said, it is a series of migration waves [5].
Quantum safety came up at the firm's annual risk and cyber risk management meeting in 2022 [1]. "Quantum safety is a resilience and risk management issue," Pfister said [12]. Questions to vendors about product roadmaps, supported algorithms, timelines and compatibility constraints started in 2023 or 2024 [6], one to two years after that meeting [17]. SiliconANGLE's account of the live pilot is dated September 17, 2026 [15], so roughly four years passed between the first risk conversation and one customer-facing system running hybrid keys [16].
This is a single interview, given at DigiCert's own event, for which theCUBE is a paid media partner; SiliconANGLE says sponsors have no editorial control over its content [14]. The account does not say how much of LGT's cryptographic estate the inventory now covers, or when the later waves land [18].
Pfister said the key question for leadership was straightforward: "Which information must remain confidential long enough that it may be exposed to a future cryptographic break?" [11] For a team doing this in its own shop, that sorts the queue, along with who ships the change, your team or a supplier. Short-lived data on systems you control is where to run the first wave and absorb the outage. Long-lived data behind firmware you cannot patch puts your date inside a supplier's release schedule, and the only lever there is the contract question about supported algorithms and compatibility constraints [6].
What to watch
- Whether LGT extends hybrid key exchange from online banking to internal PKI and vendor-supplied applications, and on what schedule.
- Whether load balancer and CDN suppliers publish supported-algorithm dates that procurement teams can hold them to.
- Whether LGT ever publishes a coverage figure for its cryptographic inventory or dates for the remaining migration waves.